For a growing SaaS company, compliance can quickly become a maze of cloud settings, access reviews, policies, vendor records, code scans, and audit evidence. The right security tools for SaaS compliance make that work easier to manage and expose gaps before an auditor or customer discovers them.
No platform can make a business compliant on its own. SOC 2 is an independent CPA examination and report, not a certification. ISO 27001 certification is issued by an external certification body, while the U.S. Department of Health and Human Services does not recognize private HIPAA certifications. Software can automate monitoring and evidence collection, but the company still owns its controls, risk decisions, and remediation.
The products below are not direct substitutes. Some run the compliance program; others secure the cloud, code, identities, or personal data behind it.
1. Vanta: Best Overall for Compliance Automation
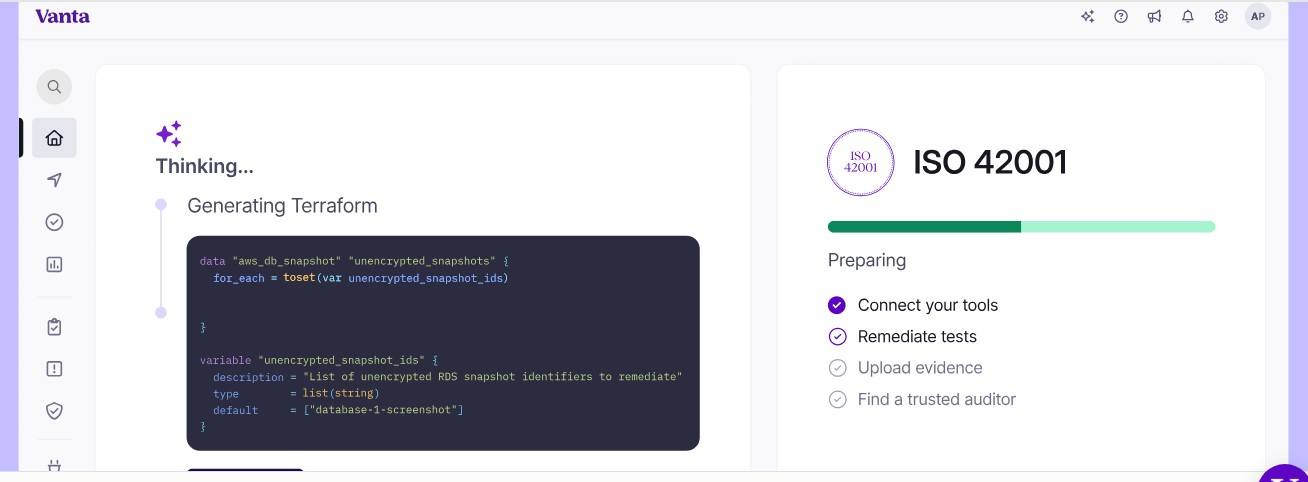
Vanta is a practical all-round option for SaaS companies working toward SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, and other programs. It connects with cloud, identity, HR, endpoint, ticketing, and development systems to collect evidence and monitor mapped controls.
The platform also covers policies, risks, vendor reviews, audits, security questionnaires, and trust centers. It suits startups and mid-sized companies that want one central compliance workspace. Its automated tests still require attention: Vanta can flag a failed control, but your team must investigate and fix the underlying problem.
2. Drata: Best for Scaling Continuous Compliance
Drata combines automated evidence collection with continuous control monitoring, risk management, vendor oversight, audit workflows, questionnaires, and customer-facing trust features. It is well suited to SaaS businesses expanding from one framework into a larger compliance program.
Its value depends on thoughtful configuration. Control owners, evidence sources, testing frequency, and framework mappings must reflect how the company actually operates. A poorly configured dashboard can look reassuring while overlooking controls outside its connected systems.
3. Secureframe: Best for Regulated SaaS Companies
Secureframe supports common commercial programs such as SOC 2, ISO 27001, HIPAA, PCI DSS, and GDPR, along with government-focused requirements including CMMC, FedRAMP, NIST frameworks, GovRAMP, and CJIS.
It provides evidence automation, control monitoring, policies, risk assessments, vendor management, personnel workflows, questionnaires, and audit preparation. This breadth makes it useful for SaaS vendors selling to healthcare, finance, government, or defense customers. Framework support does not itself deliver a FedRAMP authorization, CMMC assessment result, or certification; those processes have separate scoping and assessor requirements.
4. Sprinto: Best for Lean Cloud-Native Teams
Sprinto is designed to help cloud-based companies run compliance programs without building a large internal GRC team. It centralizes controls, collects evidence from connected services, monitors tests, and supports risks, policies, vendors, audits, questionnaires, and trust workflows.
It is a strong fit when its native integrations match the company’s stack. Buyers should test what each integration actually retrieves. A logo on an integrations page is less important than whether the connection produces complete, auditor-usable evidence.
5. Thoropass: Best for Readiness and Audit Support
Thoropass combines compliance software with professional services and audit offerings. Its platform supports control management, evidence collection, policies, audit preparation, and ongoing monitoring. Depending on the engagement, services may also include penetration testing and vulnerability assessment.
This joined-up model can reduce handoffs for a team that wants more guidance than self-service software provides. Before signing, confirm the assessment scope, testing approach, audit timeline, remediation responsibilities, deliverables, and how advisory work is separated from independent assurance.
6. Scrut Automation: Best for Risk-Led Compliance
Scrut Automation brings controls, risks, policies, evidence, vendors, and audit work into a single GRC environment. It is especially relevant for SaaS organizations managing several frameworks and wanting to connect compliance activity with business risk.
Its AI-assisted capabilities can help with policies, gaps, evidence, vendor reviews, and audit preparation. These outputs need human review. A quickly generated policy has little value if it describes an ideal process instead of the one employees genuinely follow.
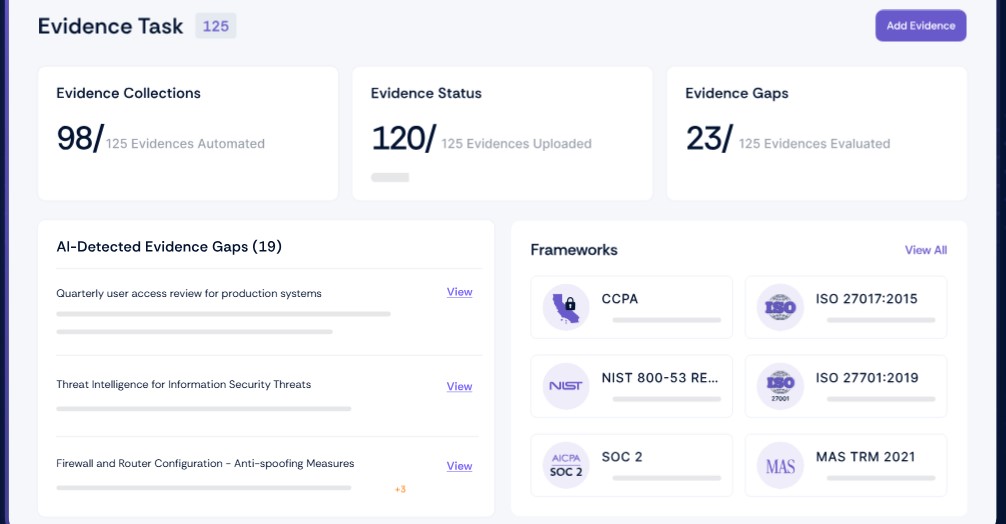
7. Wiz: Best for Cloud Security Visibility
Wiz is a cloud security platform, not a complete compliance-management system. It provides visibility into cloud misconfigurations, vulnerabilities, identities, exposed data, containers, Kubernetes, and infrastructure as code. Its security graph helps show how separate weaknesses can combine into a serious attack path.
Wiz can map technical findings to compliance requirements and produce useful cloud-control evidence. It does not replace policies, employee training, risk approvals, or audit coordination, so it often works best beside a broader GRC platform.
8. Snyk: Best for Application Security
Snyk helps development teams find weaknesses in proprietary code, open-source dependencies, containers, infrastructure-as-code files, and exposed secrets. By integrating checks into development workflows, it can produce credible evidence for secure coding, dependency governance, vulnerability management, and remediation.
Snyk is not an audit workspace. Its findings require prioritization, ownership, and realistic remediation rules; otherwise, teams may collect alerts faster than they can resolve them.
9. Okta Identity Governance: Best for Access Controls
Okta Identity Governance helps answer a recurring audit question: who has access to what, why do they have it, and who approved it? Its capabilities include access requests, lifecycle workflows, access reviews, and reporting. Combined with single sign-on and multifactor authentication, it can strengthen onboarding, role changes, offboarding, and least-privilege controls.
Automation cannot correct poor role design or applications left outside the identity system. Accurate ownership and regular review remain essential.
10. OneTrust: Best for Privacy and Data Governance
OneTrust is a strong choice when compliance depends heavily on how personal data is collected, used, shared, and retained. Depending on the modules selected, it can support data inventories, data mapping, privacy assessments, data-subject requests, vendor privacy reviews, and incident workflows.
Its breadth suits larger SaaS companies operating across jurisdictions. Early-stage businesses should define their privacy needs carefully, since a broad enterprise platform can create unnecessary cost and administrative work if only a few functions are required.
Build a Compliance Stack That Reflects Reality
The best compliance stack is not the one with the most frameworks or dashboards. It is the one that accurately reflects how your company manages access, code, infrastructure, vendors, employees, and customer data.
Choose a broad platform when evidence and coordination are the main obstacles. Add specialist security tools where technical controls need deeper coverage. Most importantly, treat every automated result as a signal, not proof that the risk has disappeared. Compliance becomes useful when it improves daily operations, not merely the appearance of an audit report.
Frequently Asked Questions on Security Tools for SaaS Compliance
1. What is the best SaaS compliance tool for a startup?
Vanta, Drata, Secureframe, and Sprinto are all credible choices. The best option depends on the required framework, technology stack, internal expertise, budget, and preferred level of guidance. Test finalists with your real systems instead of choosing from feature counts alone.
2. Can compliance software guarantee SOC 2, ISO 27001, or HIPAA compliance?
No. It can organize controls, collect evidence, and identify selected failures. It cannot guarantee that controls are well designed, consistently followed, or sufficient for every legal and contractual obligation.
3. Is Vanta better than Drata?
Neither is universally better. Compare integration depth, control customization, audit workflow, reporting, support, usability, and total cost. The better platform is the one your team can maintain accurately after the first audit.
4. How much do SaaS compliance tools cost?
Pricing usually varies by company size, frameworks, modules, integrations, and support level. Budget separately for auditors, penetration tests, certification bodies, remediation, and employee time. The subscription price is rarely the complete compliance cost.
5. Does a SaaS company need more than one security tool?
Not necessarily. A smaller company may combine one compliance platform with controls already available in its cloud, identity, endpoint, and development systems. Specialist platforms become more valuable as infrastructure, regulatory exposure, and customer expectations grow.