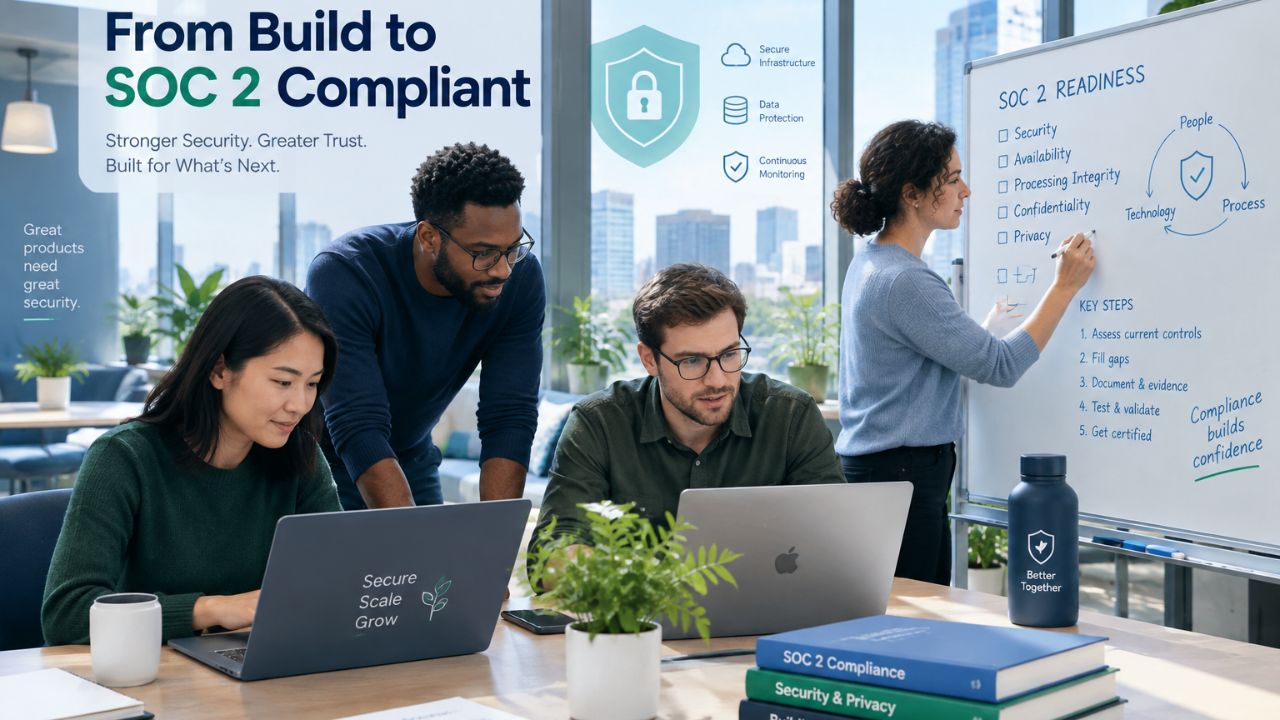
Your first SOC 2 request usually shows up in the middle of a deal. A bigger client sends a security questionnaire and asks, “Can you share your SOC 2 report?” If you don’t have one, the deal slows down. Preparing SaaS startup for SOC2 compliance takes planning, but a small team can do it without a big budget.
I’m Sayedul Haq Mihir, Chief Technical Advisor at ImagineLab.art. This guide comes from my general advisory work with SaaS teams, not from a single audit. I’ll share what usually triggers SOC 2, what to fix first, and where small teams tend to get stuck.
One quick note: I’m not an auditor. Only a licensed CPA firm can run your SOC 2 audit, so confirm scope and timing with them.
What to Know Before Preparing SaaS Startup for SOC2 Compliance
SOC 2 isn’t a certificate you download. You earn it by passing an audit, which must be done by a licensed CPA or CPA firm that checks your controls against the AICPA’s Trust Services Criteria.
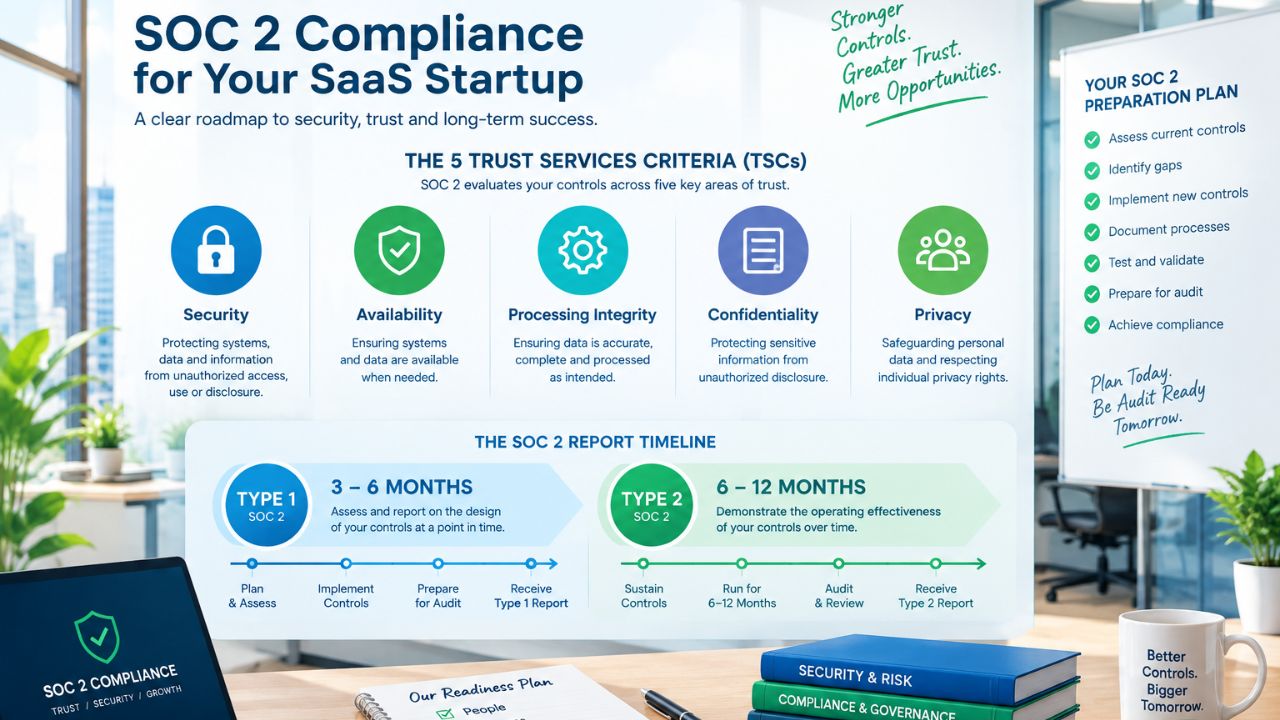
There are five criteria: Security, Availability, Processing Integrity, Confidentiality, and Privacy. Security is required in every audit. You add the others based on what you promise customers and what buyers ask for.
The rules haven’t changed much. As of 2026, the standard is still the 2017 criteria with the points of focus revised in 2022. AICPA’s 2026 proposals affect how auditors do their work, not the criteria themselves. Be careful with any vendor selling “new SOC 2 requirements.”
You’ll also need to choose a report type:
- Type 1 checks whether your controls are designed correctly on a single date.
- Type 2 checks whether those controls actually worked over an observation period of three to twelve months.
Steps for Preparing SaaS Startup for SOC2 Compliance
Step 1 of Preparing SaaS Startup for SOC2 Compliance: Ask the Client What They Need
In my experience, the trigger is almost always an enterprise or agency client asking for a report. Before you do anything else, ask them two questions. Will a Type 1 report work for now? Which criteria do they care about?
Don’t guess. Ask the prospect what they’ll accept before you pay for the faster report. If a Type 1 gets the deal moving, start the Type 2 observation period right away so you don’t have to repeat the prep work.
Step 2 of Preparing SaaS Startup for SOC2 Compliance: Keep the Scope Small
Most SaaS teams I advise start with Security, then add Availability or Confidentiality. Add Availability if clients depend on your uptime. Add Confidentiality if you handle their private files or business data.
Scope also means systems, not just criteria. List only the production systems that touch customer data. Your hosting provider is part of that picture. When you compare options, ask each one for its own SOC 2 report. My list of the best hosting providers for SaaS startups is a good starting point.
Step 3 of Preparing SaaS Startup for SOC2 Compliance: Run a Gap Check in a Spreadsheet
You don’t need expensive software to start. I’ve seen spreadsheets and plain internal docs work well for small teams. Make one row per control with these columns: what the control is, who owns it, current status, and where the evidence lives.
Compliance platforms like Vanta, Drata, Secureframe, and Sprinto can cut down manual evidence work, but only if your auditor actually uses their exports. Get the spreadsheet in order first. Buy a platform later if manual work becomes the bottleneck.
Step 4 of Preparing SaaS Startup for SOC2 Compliance: Turn On MFA and Review Access
This step fixes the most common gaps fast. Auditors and clients in 2026 expect MFA, least-privilege access, and regular access reviews.
- Turn on MFA everywhere: email, cloud console, code repository, databases, and admin panels.
- Give each person only the access their job needs.
- Review access on a fixed schedule and remove anyone who has left or changed roles.
- Save a record of each review, such as a dated sheet or a screenshot.
These controls are easier to build if they’re part of your stack from day one. My guide on choosing a tech stack for a SaaS startup covers how to plan for that early.
Step 5 of Preparing SaaS Startup for SOC2 Compliance: Set Up Audit Logging
If something isn’t logged, you can’t prove it happened. Auditors may ask for detailed evidence like monitoring logs, incident response records, and vendor risk assessments.
Log who signs in, who changes permissions, and who deploys code. Keep the logs somewhere team members can’t quietly edit them. Then check that the logs actually contain what you expect before an auditor looks.
Step 6 of Preparing SaaS Startup for SOC2 Compliance: Write Short Policies People Will Follow
For small teams, this is one of the hardest parts. Most founders either copy a 40-page template nobody reads or put off writing anything at all.
Write short policies that match how you really work. Start with access control, change management, incident response, vendor management, and employee onboarding and offboarding. If a policy says you review access every quarter, you have to actually do it every quarter. Auditors test what’s written.
Avoid policies and approval steps nobody can keep up after the audit. A simple rule your team follows beats a strict rule they ignore.
Step 7 of Preparing SaaS Startup for SOC2 Compliance: Collect Evidence Every Week
Evidence collection is the other hard part. Teams usually do the work but forget to save proof of it. Then someone spends days rebuilding records before the audit.
Make a folder for each control. Drop in proof as tasks happen: access review sheets, approved code changes, incident notes, and training records. Access reviews, change approvals, vendor assessments, and incident logs all need to happen regularly and be recorded throughout the observation period.
Step 8 of Preparing SaaS Startup for SOC2 Compliance: Check Your Vendors
Every tool that touches customer data is part of your risk. List your vendors, what data each one handles, and whether it has its own SOC 2 or similar report. Include your payment processor too. If you sell in the region, my guide to payment gateways for SaaS startups in South Asia can help you compare options.
The Team Problem in Preparing SaaS Startup for SOC2 Compliance
Tools and documents are the easy part. The real challenge is getting a small team to follow new habits. Developers are used to moving fast, and suddenly they need approvals and a record of every change.
What usually works:
- Name one owner. A common mistake is buying readiness help, software, and the audit from separate vendors with nobody owning the deadline.
- Explain the reason. Tell the team this report is what unlocks bigger clients.
- Build it into existing tools. Put approvals inside the pull request process instead of a separate form.
- Check in each week. A five-minute review catches missed steps early.
Keeping Up After Preparing SaaS Startup for SOC2 Compliance
SOC 2 isn’t a one-time project. Reports are treated as valid for 12 months, so you’ll need to keep monitoring your controls.
If your report runs out before the next audit finishes, management can issue a bridge letter to cover the gap. A bridge letter is temporary, though, and it doesn’t replace a valid SOC 2 report. Plan your next audit window early.
A readiness assessment is also worth doing before the formal audit. It’s an optional trial run where an experienced auditor finds gaps first.
Final Thoughts
Preparing SaaS startup for SOC2 compliance is less about buying tools and more about building habits you can prove. Start with the client’s actual request. Keep the scope tight, turn on MFA, review access, log what matters, and write policies your team will follow. This week, open a spreadsheet, list your controls, and pick one owner. That first step gets you further than any template.