

The U.S. Secret Service has confirmed that it dismantled a large and sophisticated network of electronic devices in the New York tri-state area that posed a direct threat to U.S. officials and national security. The operation took place just days before world leaders gathered in Manhattan for the United Nations General Assembly, raising concerns about both timing and intent.
Scale of the Discovery
During the operation, investigators uncovered more than 300 co-located SIM servers and over 100,000 SIM cards spread across multiple sites. According to the Secret Service, these devices were strategically concentrated within a 35-mile (56-kilometer) radius of the U.N. headquarters in New York City.
The dismantling was conducted under the authority of the agency’s Advanced Threat Interdiction Unit, a specialized division tasked with intercepting emerging threats to communications infrastructure. The investigation is being supported by several federal and local partners, including the Department of Homeland Security, the Department of Justice, the Office of the Director of National Intelligence, and the New York Police Department.
Potential Capabilities of the Device Network
Authorities explained that the network was far more dangerous than a simple collection of telecommunication equipment. Its functionality gave it the potential to serve as a disruptive weapon against critical infrastructure in several ways:
-
Telecom sabotage: By leveraging thousands of SIM cards simultaneously, attackers could disable or overload cell towers, effectively cutting service to large portions of the population.
-
Denial-of-service attacks: The servers were capable of launching high-volume traffic floods, overwhelming carriers’ networks with millions of text messages or calls in minutes. Experts note that such traffic spikes could prevent emergency responders from communicating during crises.
-
Encrypted communication channels: The system could have been used as a covert hub for criminal enterprises or nation-state actors to exchange information securely and without easy traceability.
-
Threat transmission: Investigators confirmed the devices had already been exploited to send anonymous threats against U.S. officials, escalating the urgency of the investigation.
Cybersecurity specialists described this type of infrastructure as a SIM farm—a massive installation that can run tens of thousands of mobile connections simultaneously. In some configurations, SIM farms can process as many as 30 million text messages per minute, making them highly effective for spam, fraud, or coordinated attacks.
Safehouses and Geographic Spread
The investigation also uncovered a network of electronic safehouses designed to host and hide these devices. Many of these were discovered abandoned at the time of the raids. Locations included:
-
Armonk, New York
-
Greenwich, Connecticut
-
Queens, New York
-
Multiple unidentified sites in New Jersey
According to reports from CNN and NBC News, these locations were rented specifically for the purpose of hosting the servers and cards. The empty state of several safehouses suggested that operators were prepared to relocate quickly if law enforcement drew near.
Links to Foreign Actors and Criminal Enterprises
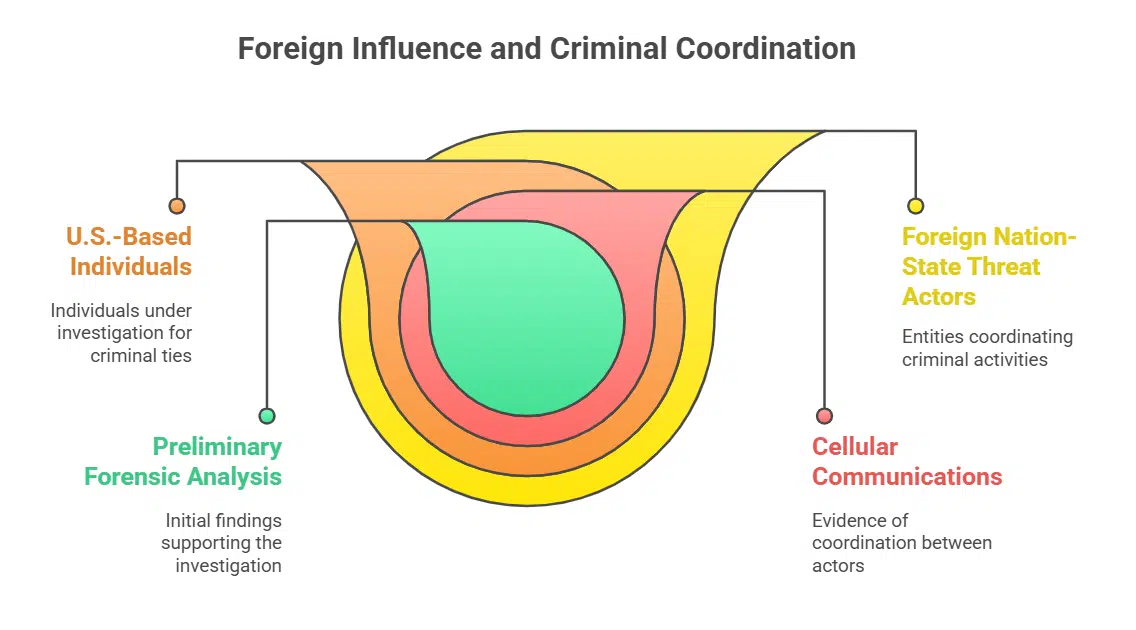
Preliminary forensic analysis pointed to active cellular communications between foreign nation-state threat actors and individuals already under investigation by federal law enforcement. While the Secret Service has not publicly identified which nations or groups may have been involved, officials confirmed that the communications showed signs of coordination between foreign operatives and U.S.-based individuals tied to criminal activity.
The probe is ongoing, and officials are withholding details on the exact nature of the threats issued, the U.S. officials who were targeted, and whether the threats were credible assassination plots or broader intimidation attempts.
Additional Seizures During the Operation
Beyond the telecommunication devices, law enforcement officers reportedly seized other suspicious items from certain safehouses, including illegal firearms and quantities of narcotics. Early reports indicated that investigators confiscated around 80 grams of cocaine, raising the possibility that the network’s operators were tied to both organized crime and foreign intelligence.
Why the Discovery Matters
The proximity of the device network to the U.N. General Assembly was particularly alarming. Every September, New York hosts the world’s largest diplomatic gathering, bringing together presidents, prime ministers, and heads of state. Security is already among the most intense of any global event, but the presence of a hidden system capable of disrupting communications within a short distance of the U.N. amplified concerns of an imminent coordinated attack.
Had the devices been activated during the General Assembly, experts warn they could have crippled cellular communications in parts of Manhattan, leaving residents, visitors, and security services vulnerable to both panic and disorganization.
Officials also noted the timing was deliberate, suggesting the network may have been positioned not just for long-term exploitation, but for maximum disruption during one of the most sensitive diplomatic events of the year.
Understanding SIM Farms and Their Global Use
SIM farms, also known as SIM box networks, have become a global cybersecurity issue. They are often used for:
-
Telecom fraud, by routing calls and messages to avoid carrier fees.
-
Mass scams and phishing, with the ability to send millions of fraudulent texts.
-
Political disinformation campaigns, by amplifying propaganda at scale.
-
Covert state operations, where they provide untraceable communication channels.
In previous cases, SIM farms were dismantled in parts of Europe, Africa, and Asia, with evidence linking them to organized crime and in some cases to hostile governments. What distinguishes the New York case is the sheer scale—hundreds of servers and more than 100,000 SIM cards in a dense metropolitan area.
Next Steps in the Investigation
Forensic teams are now analyzing the recovered servers and SIM cards. Their priorities include:
-
Mapping all communication logs to identify senders, recipients, and timing of messages.
-
Establishing the financial backers of the operation, including whether shell companies were used to rent properties.
-
Identifying international linkages, particularly to known cybercriminal groups or intelligence agencies.
-
Determining whether other U.S. cities may be hosting similar hidden installations.
Experts caution that this investigation may take months or even years, given the complexity of analyzing such a massive volume of data.
The dismantling of this network underscores the increasing convergence of cybersecurity threats and physical national security risks. Unlike purely digital hacks, SIM farms directly exploit infrastructure that people depend on daily. In this case, their presence in one of the most densely populated regions of the U.S.—and near a global diplomatic event—made them especially dangerous.
While the devices are now under government control, analysts believe this may only be the beginning of wider operations aimed at uncovering other hidden telecom farms inside the country. Officials are preparing for the possibility of additional takedowns in the coming months.
The U.S. Secret Service’s action against this SIM-based network is one of the largest counter-telecom operations ever reported in the United States. The seizure of 300 servers, 100,000 SIM cards, weapons, and narcotics revealed how such networks can serve both geopolitical and criminal agendas.
Although investigators have not disclosed which officials were targeted or which nations were behind the threats, the evidence of foreign communication links has heightened concerns about cross-border interference in U.S. security.
The case highlights both the vulnerabilities of modern telecommunications and the ongoing challenges of protecting national infrastructure in an era where digital, criminal, and state threats overlap.


























