Deploying artificial intelligence in cybersecurity is no longer a separate, future innovation project—it is already embedded inside modern security tools and everyday business applications.
At its core, artificial intelligence in cybersecurity accelerates threat detection, automates incident response, and analyzes network anomalies at machine speed. However, it also creates two critical, linked challenges: adopting AI safeguards without dangerous over-automation, and defending against AI-driven attacks that arrive faster and look far more convincing.
Crucially, AI does not replace human oversight. Attackers still select targets and adapt campaigns, while human defenders must interpret evidence and make high-stakes decisions. By shifting the economics of digital warfare, AI exposes slow patching, weak identity controls, and incomplete network monitoring.
What Artificial Intelligence in Cybersecurity Actually Changes
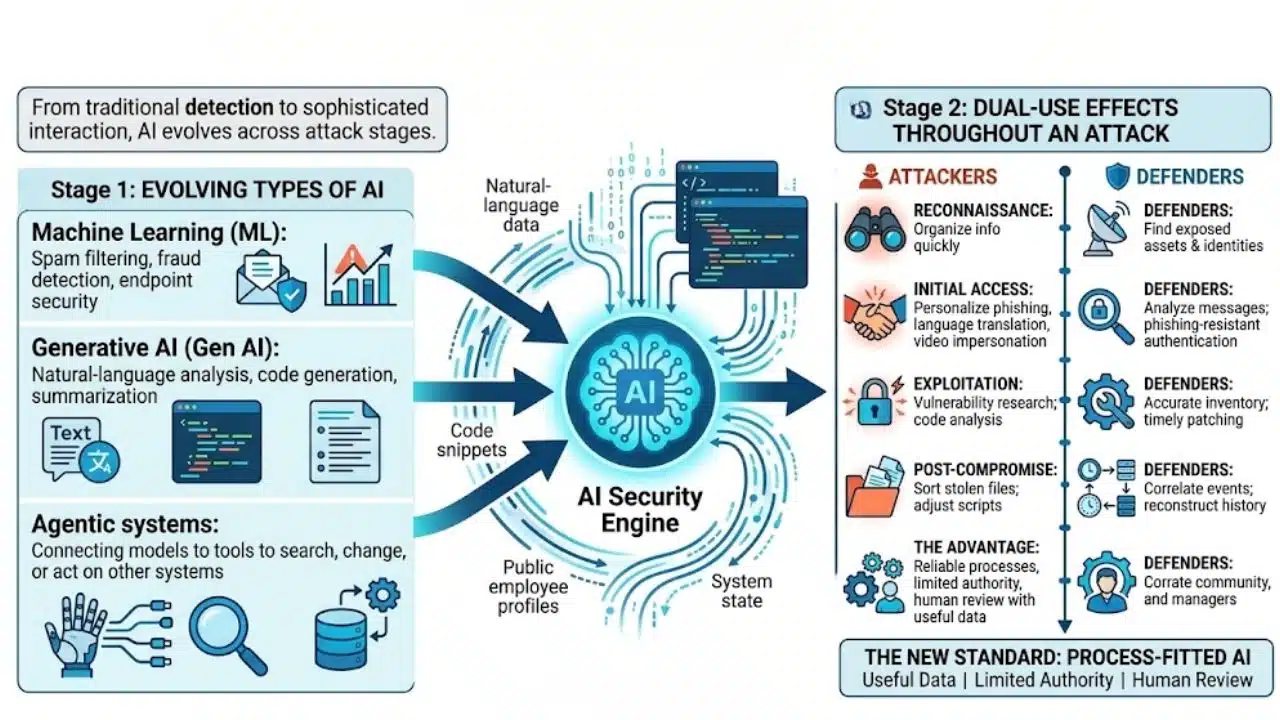
Machine learning has supported spam filtering, fraud detection, and endpoint security for years. Generative AI adds natural-language analysis, code generation, and fast summarization. Agentic systems go further by connecting models to tools that can search, change, or act on other systems.
The effects appear throughout an attack:
- Reconnaissance: Attackers can organize public information about employees, suppliers, and technology more quickly. Defenders can use similar techniques to find exposed assets and risky identities.
- Initial access: Generative tools can personalize phishing messages, translate them, and support voice or video impersonation. Defensive AI can help analyze messages, but independent verification and phishing-resistant authentication remain more dependable controls.
- Exploitation: AI can assist code analysis and vulnerability research on both sides. This makes accurate asset inventories and timely patching more valuable.
- Post-compromise activity: Attackers can sort stolen files or adjust scripts. Defenders can correlate identity, endpoint, cloud, and network events to reconstruct what happened.
The advantage comes from fitting AI into a reliable process with useful data, limited authority, and human review.
Offensive AI Makes Familiar Attacks More Efficient
Social engineering offers attackers one of the clearest gains. A criminal can draft plausible messages in several languages, vary the wording, and adjust the tone for a finance executive, employee, or supplier. Synthetic audio and video can add another layer of credibility.
In 2025, the FBI warned about malicious actors using AI-generated voice messages to impersonate senior US officials. The deception still relied on familiar methods: building trust, moving the conversation to another platform, and directing targets toward malicious links. AI improved the presentation; it did not replace the underlying fraud.
That distinction leads to practical advice. Awkward grammar is now a weaker phishing signal. A familiar voice or convincing video is not proof of identity. Payment requests, credential resets, sensitive file transfers, and changes to account access should be confirmed through a separate channel already known to the organization.
Technical use is also advancing. The UK National Cyber Security Centre identifies AI-assisted vulnerability research and exploit development as a major near-term concern. Google Threat Intelligence has documented language models being used for reconnaissance, scripting, vulnerability research, evasion, and data collection.
One example deserves careful wording. Google reported that APT28 used PROMPTSTEAL against Ukraine. The malware queried the Qwen2.5-Coder-32B-Instruct model through the Hugging Face API to generate Windows commands for collecting system information and documents. It was observed in live operations. PROMPTFLUX, a separate sample designed to use an AI model for code rewriting and obfuscation, was described as experimental and unable in its observed state to compromise a device.
Those cases show movement beyond ordinary coding assistance, but not that fully autonomous hacking is the norm. The common pattern remains human-directed operations with AI reducing research time and manual effort. Security budgets should reflect that evidence, not dramatic claims about self-running attacks.
Defensive AI Works Best as an Analyst Multiplier
Security operations centers collect more alerts and telemetry than analysts can inspect manually. AI can enrich an alert, summarize evidence, draft a query, or assemble a timeline. The UK NCSC also identifies applications in endpoint detection, vulnerability discovery, red teaming, remediation, and incident response.
Consider an unusual sign-in followed by a new PowerShell process and access to a cloud storage folder. An AI assistant could gather related identity and endpoint events and prepare an investigation summary. The analyst still has to decide whether the sequence is malicious, whether the account should be disabled, and what business activity might be interrupted.
Product demonstrations can hide this difficulty. A clean summary does not prove that the underlying conclusion is correct. Models can miss context, invent explanations, or sound certain when telemetry is incomplete. Fragmented logs and poor asset data will limit even a capable system.
For most organizations, read-only investigation support is a better starting point than autonomous containment. It offers measurable time savings without giving a probabilistic system immediate authority to isolate endpoints or change access controls.
AI Systems Create Their Own Attack Surface
An AI application includes more than its model: data stores, retrieval systems, APIs, service accounts, cloud infrastructure, and connected tools. Every connection creates another trust decision.
Prompt injection is a central risk. Hostile instructions can be placed inside a webpage, document, email, image, or retrieved knowledge source. If an assistant interprets that content as an instruction, it may expose information or misuse a connected tool. Retrieval-augmented generation and fine-tuning may improve relevance, but they do not fully prevent this problem. A system prompt should never be the only security control.
Other risks include data poisoning, model evasion, sensitive-information disclosure, insecure dependencies, and attacks against accounts and APIs. Agentic systems raise the stakes because a faulty response can become an action. Broad permissions, untrusted input, and no approval gate are a dangerous combination.
A Practical Enterprise Strategy
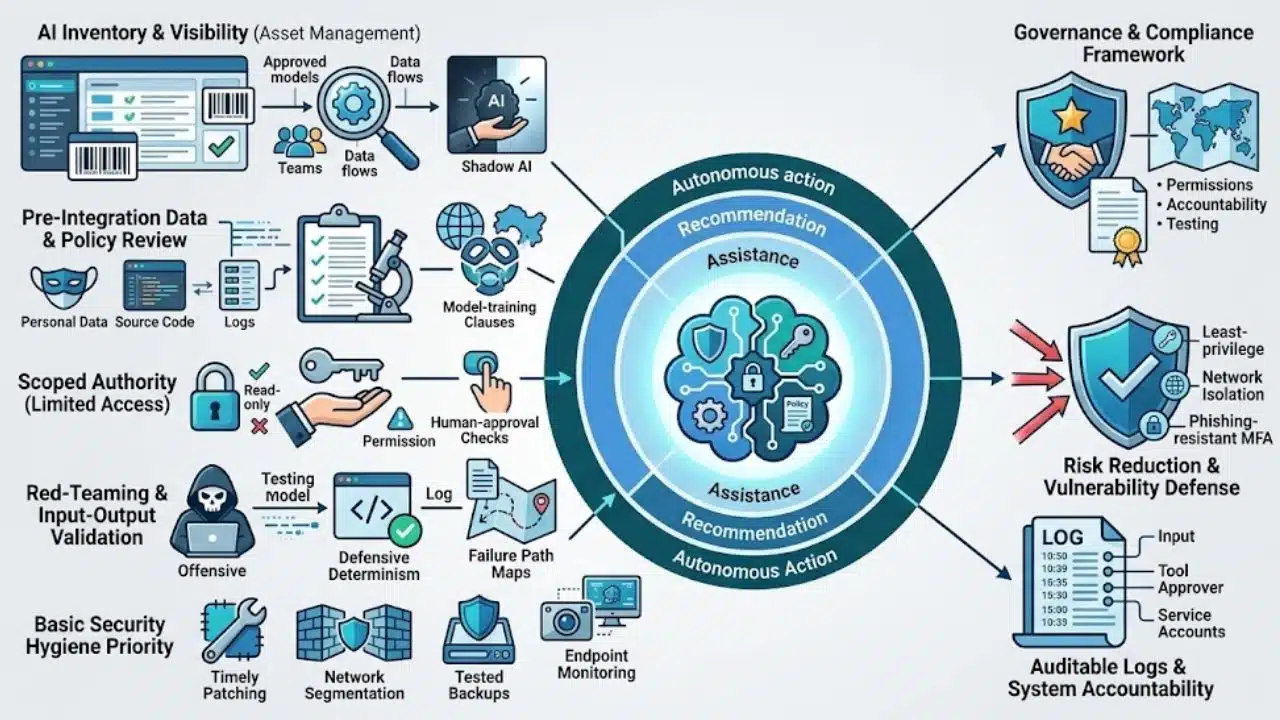
A workable plan separates assistance, recommendations, and autonomous action. Each level needs different permissions, tests, and accountability.
- Inventory AI use and ownership. Record approved models, embedded features, data flows, integrations, service accounts, and responsible teams. Shadow AI is partly an asset-management problem: security cannot assess systems it cannot see.
- Check the data before connecting it. Security logs may contain personal data, source code, access tokens, internal hostnames, and customer information. Review provider retention, model-training terms, regional processing, tenant isolation, and administrative access.
- Start with limited authority. Use scoped credentials, allowlisted tools, and read-only access where possible. Require human approval for actions that are destructive, privileged, financial, or visible outside the organization.
- Treat model input and output as untrusted. Validate structured responses with deterministic code. Red-team the model, retrieval layer, APIs, tools, identity controls, and failure paths. Logs should show what information entered the system, which tool it called, and who approved the action.
- Do not trade basic security for AI spending. Timely patching, network segmentation, tested backups, endpoint monitoring, least privilege, and phishing-resistant multifactor authentication still address many of the weaknesses AI-assisted attacks exploit.
Measure Security Outcomes, Not AI Activity
Prompt counts and generated summaries say little about risk reduction. Track alert precision, time to triage, time to contain, analyst overrides, missed detections, and unsafe actions blocked by policy. Record incidents involving the AI service itself, including data exposure, prompt injection, unauthorized use, and unexpected tool calls. If a deployment produces faster reports but no better decisions, it has improved presentation rather than security.
Final Thoughts
Artificial intelligence in cybersecurity rewards teams that can move quickly without surrendering control. A sensible first step is to choose one bounded, read-only workflow, define how success will be measured, and test it with incomplete and hostile inputs before expanding access.
AI can make a mature security program faster and more capable. It cannot repair missing assets, weak authentication, slow patching, or unclear accountability. Those foundations should decide how far automation is allowed to go.
FAQs
Can AI replace cybersecurity analysts?
Not across the full job. It can reduce repetitive work and prepare evidence, but investigations still involve uncertain context, business consequences, and accountability. Skilled analysts remain responsible for those judgments.
Does every organization need AI in its security operations center?
No. A team with fragmented telemetry, poor asset records, or an unmanageable alert backlog may get more value from fixing those problems first. AI is useful when it improves a defined workflow, not when it is added simply because a vendor includes it.
What should a company check before giving an AI assistant access to security logs?
Check data content, retention, model-training terms, processing location, tenant isolation, administrator access, and deletion controls. Give the assistant only the data and permissions required for its task.